Put guardrails between your LLM and your users
Inspect risky prompts, mask sensitive data, and review AI decisions with audit-ready logs.
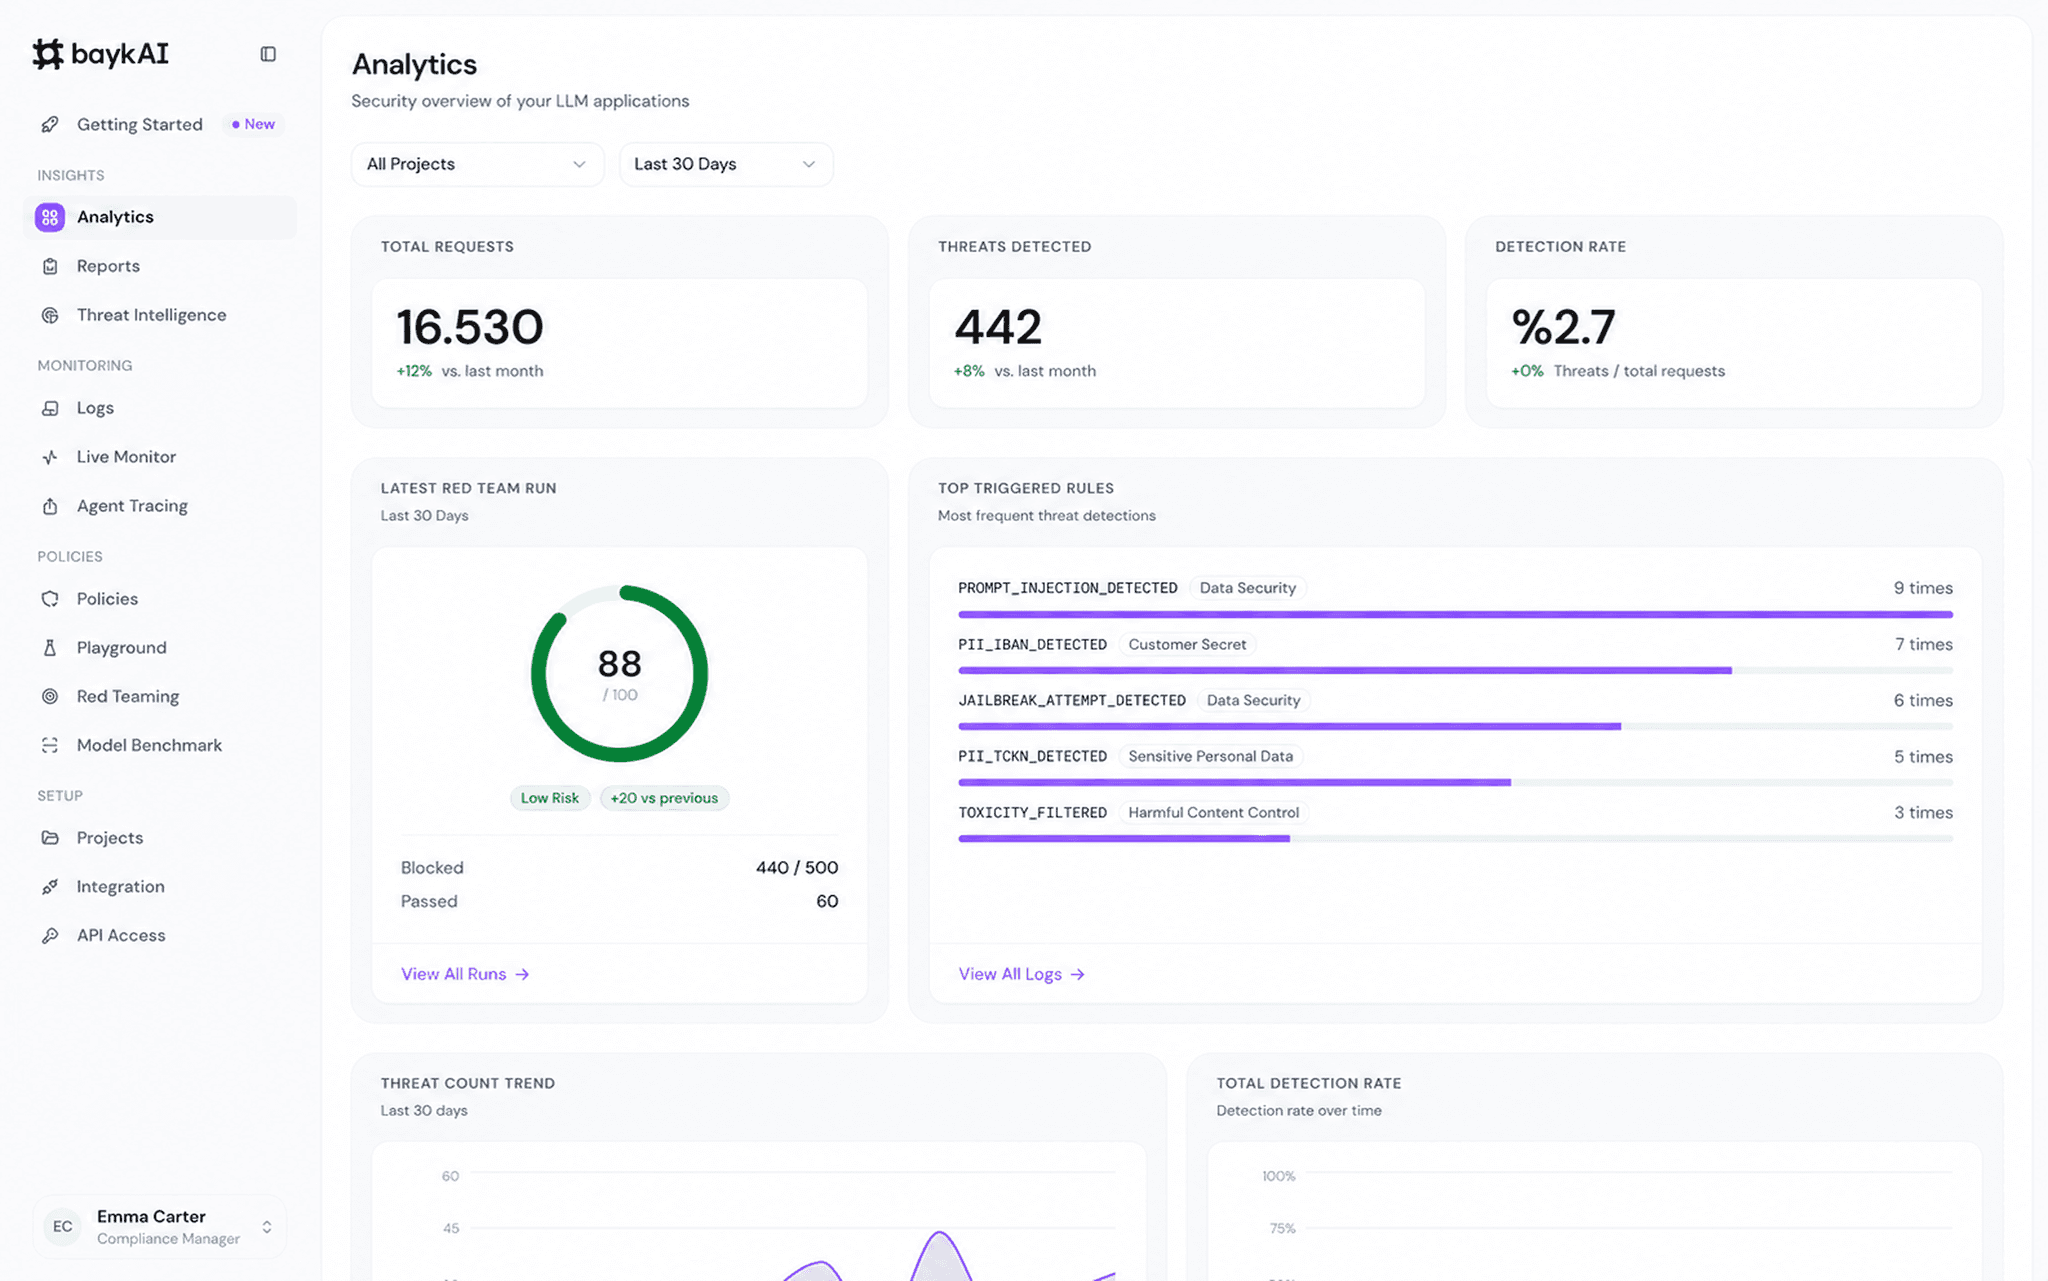
AI teams need control, not just speed
Every prompt, response, and agent action can introduce security, privacy, and compliance risk.
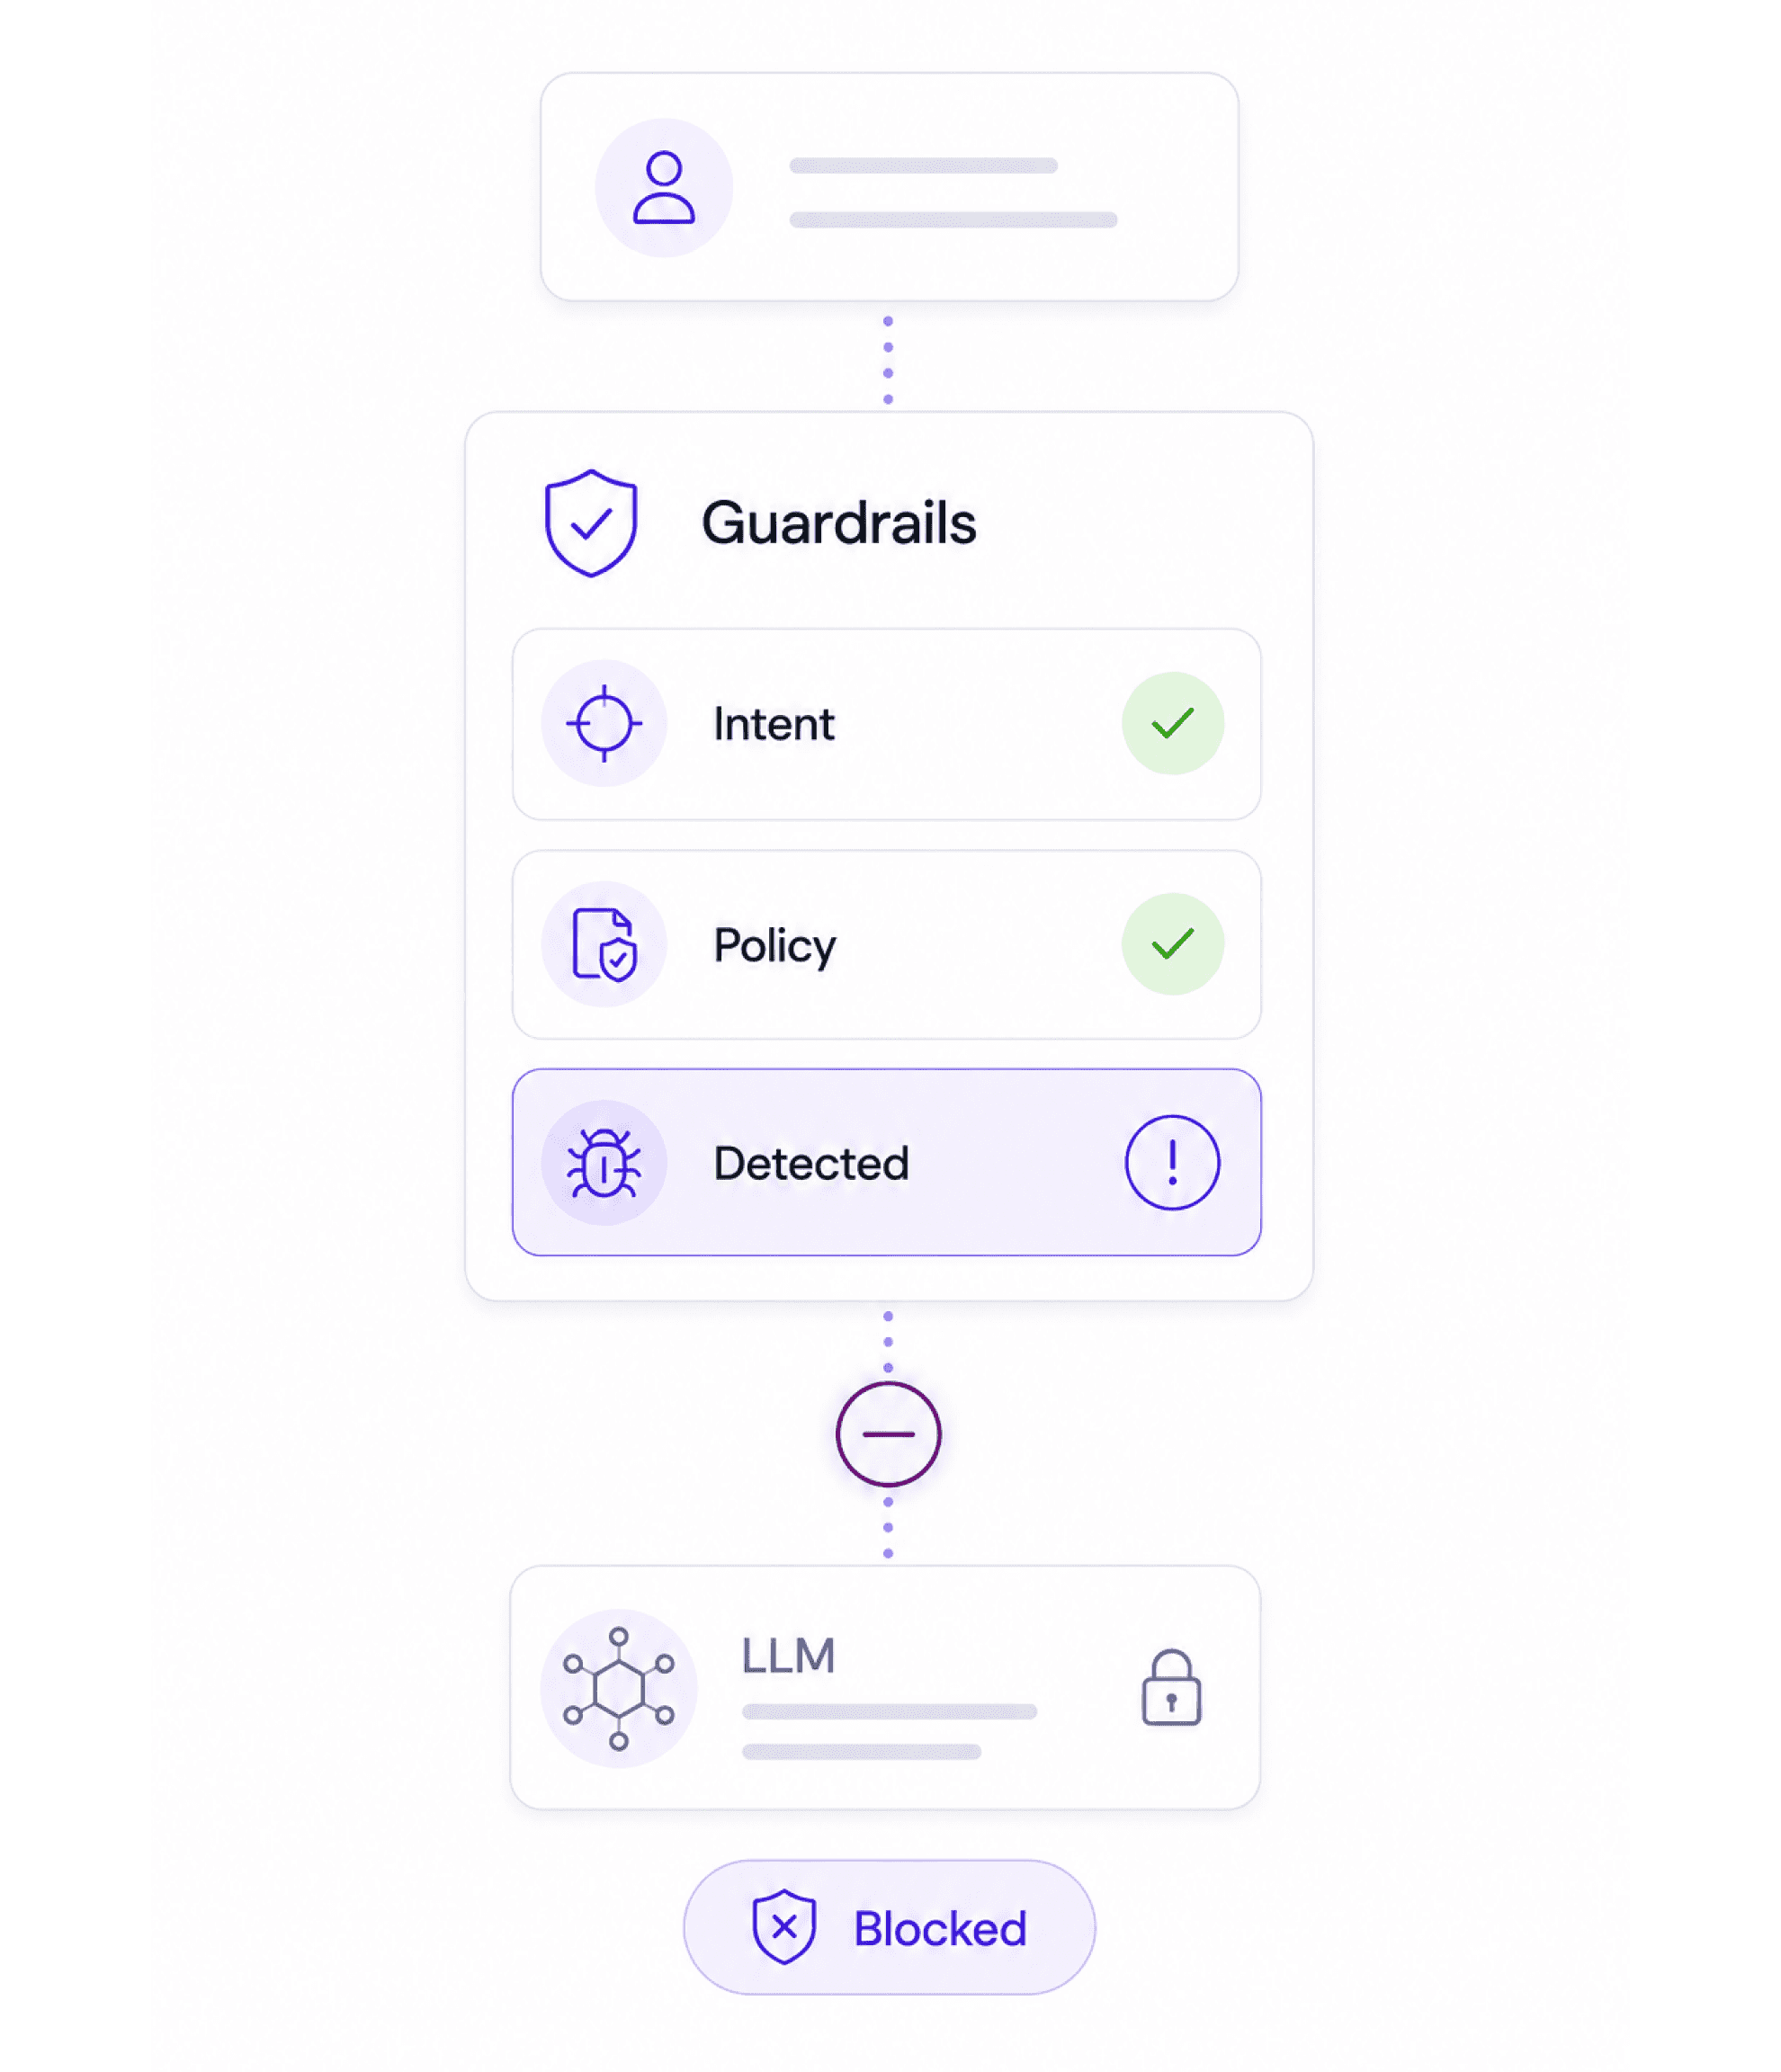
Prompt injection
Identify jailbreak attempts and malicious instructions before they affect your AI workflow.
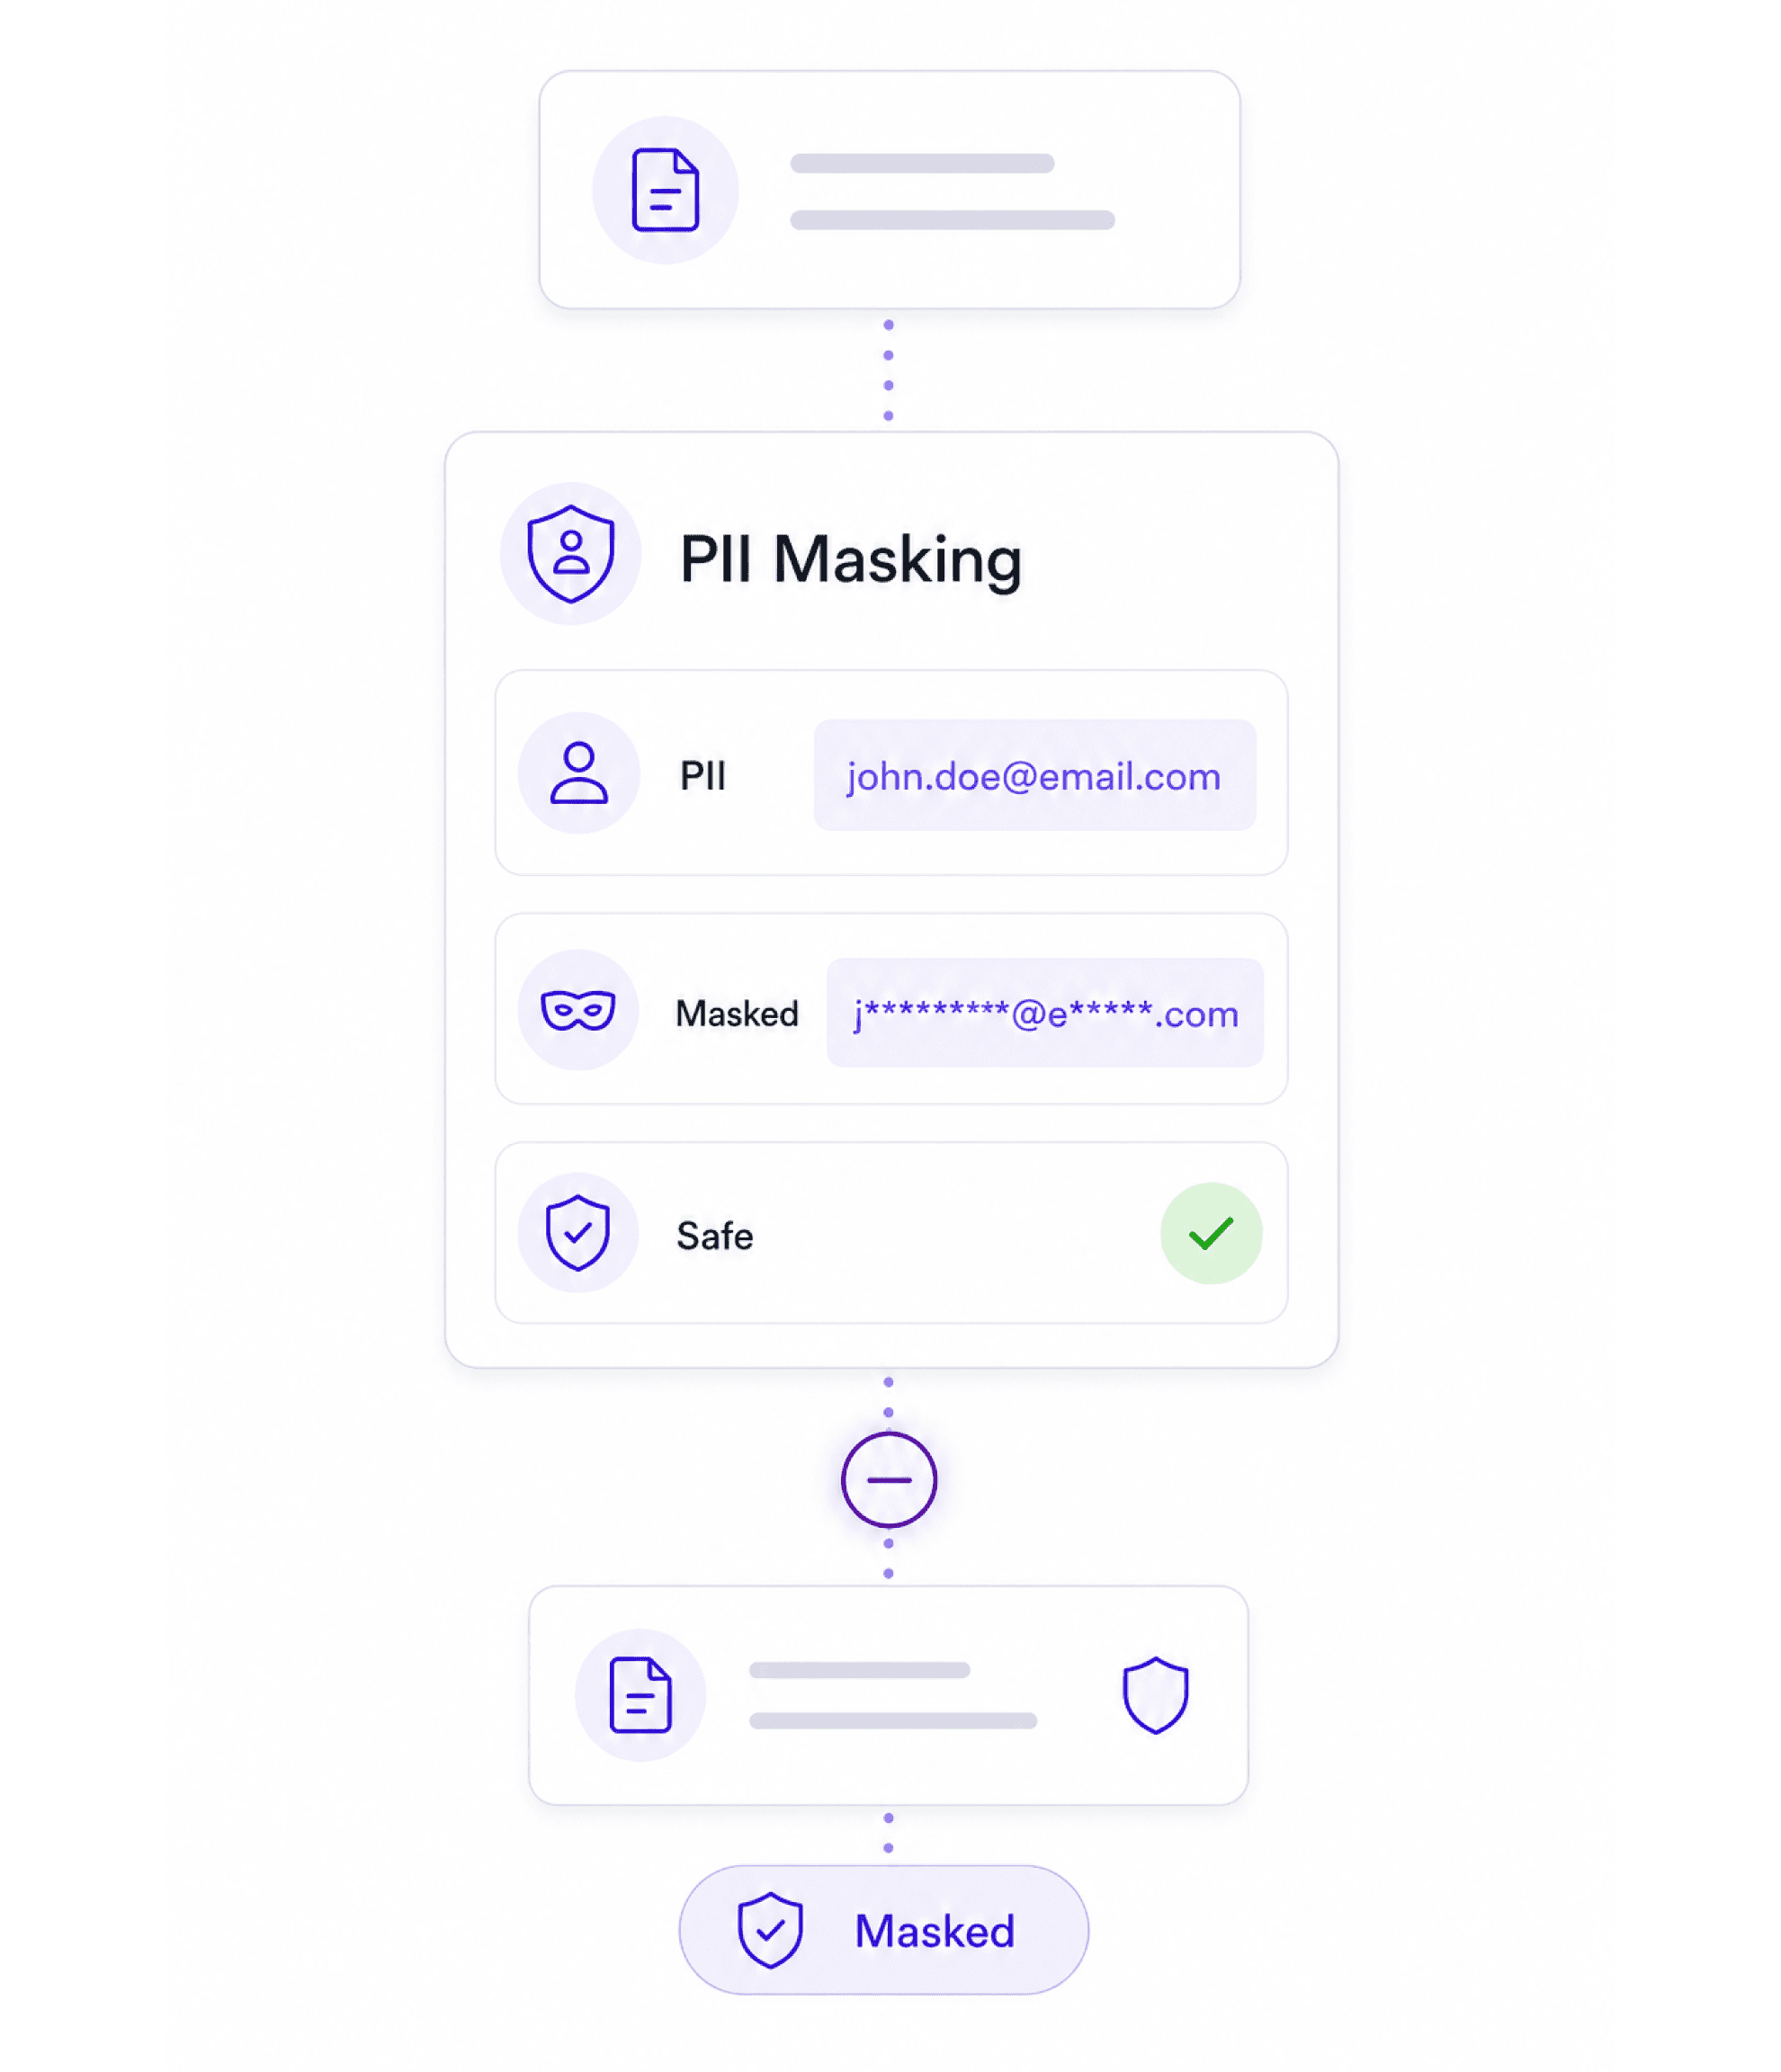
Sensitive data leakage
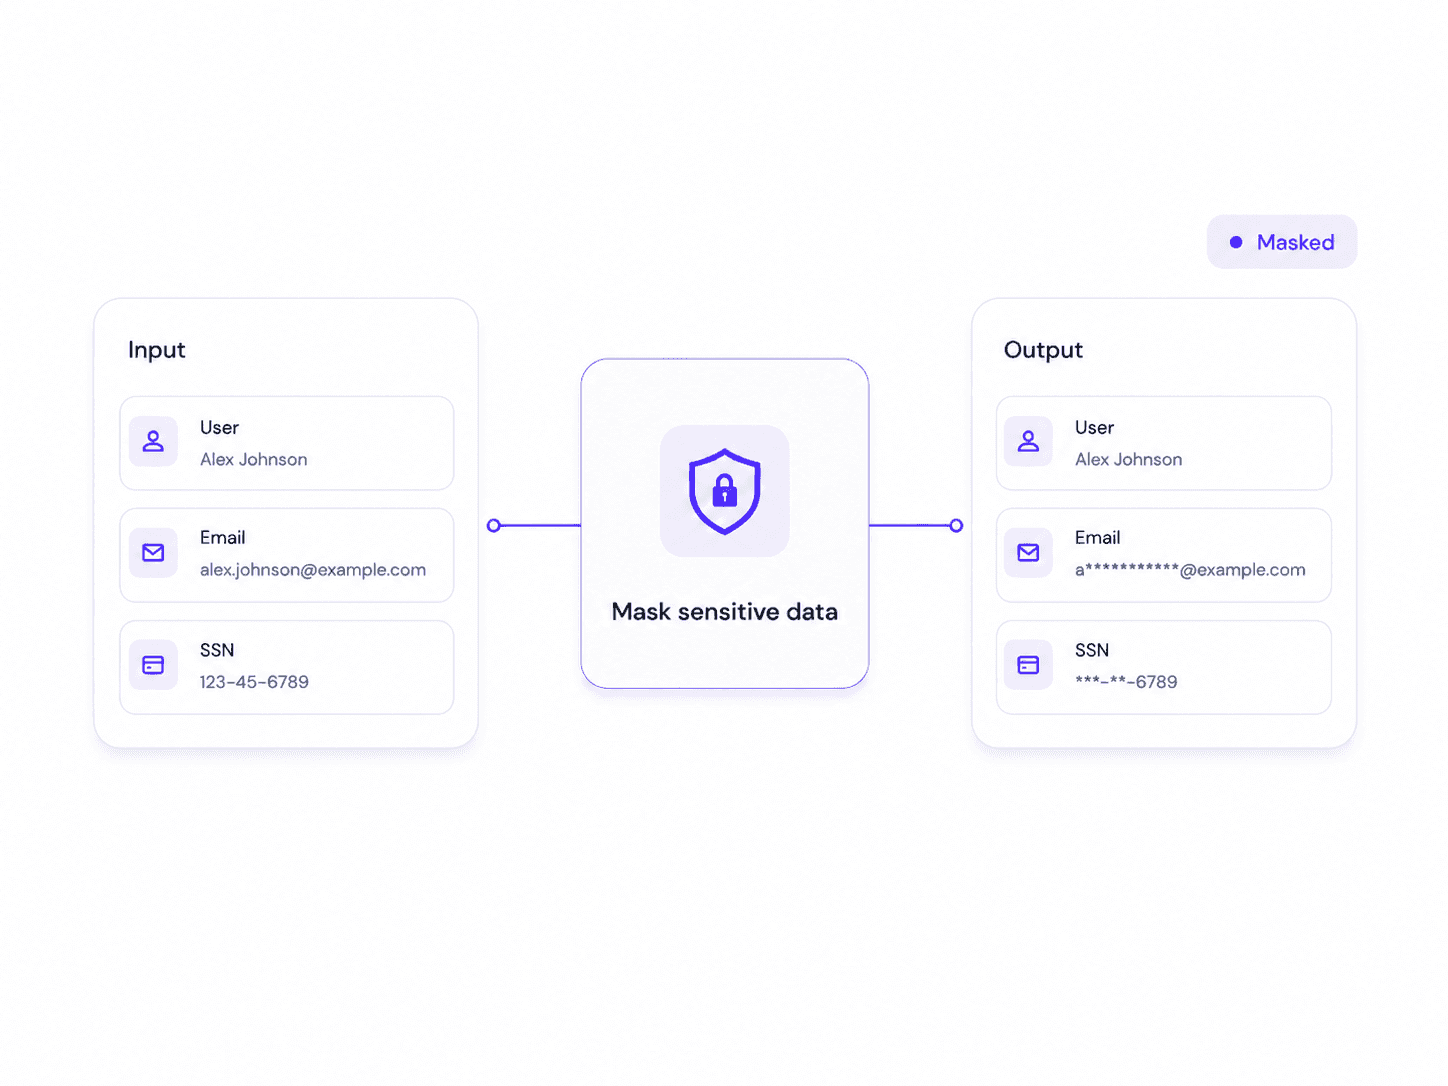
Mask personal data, financial identifiers, and secrets before they appear in prompts or logs.
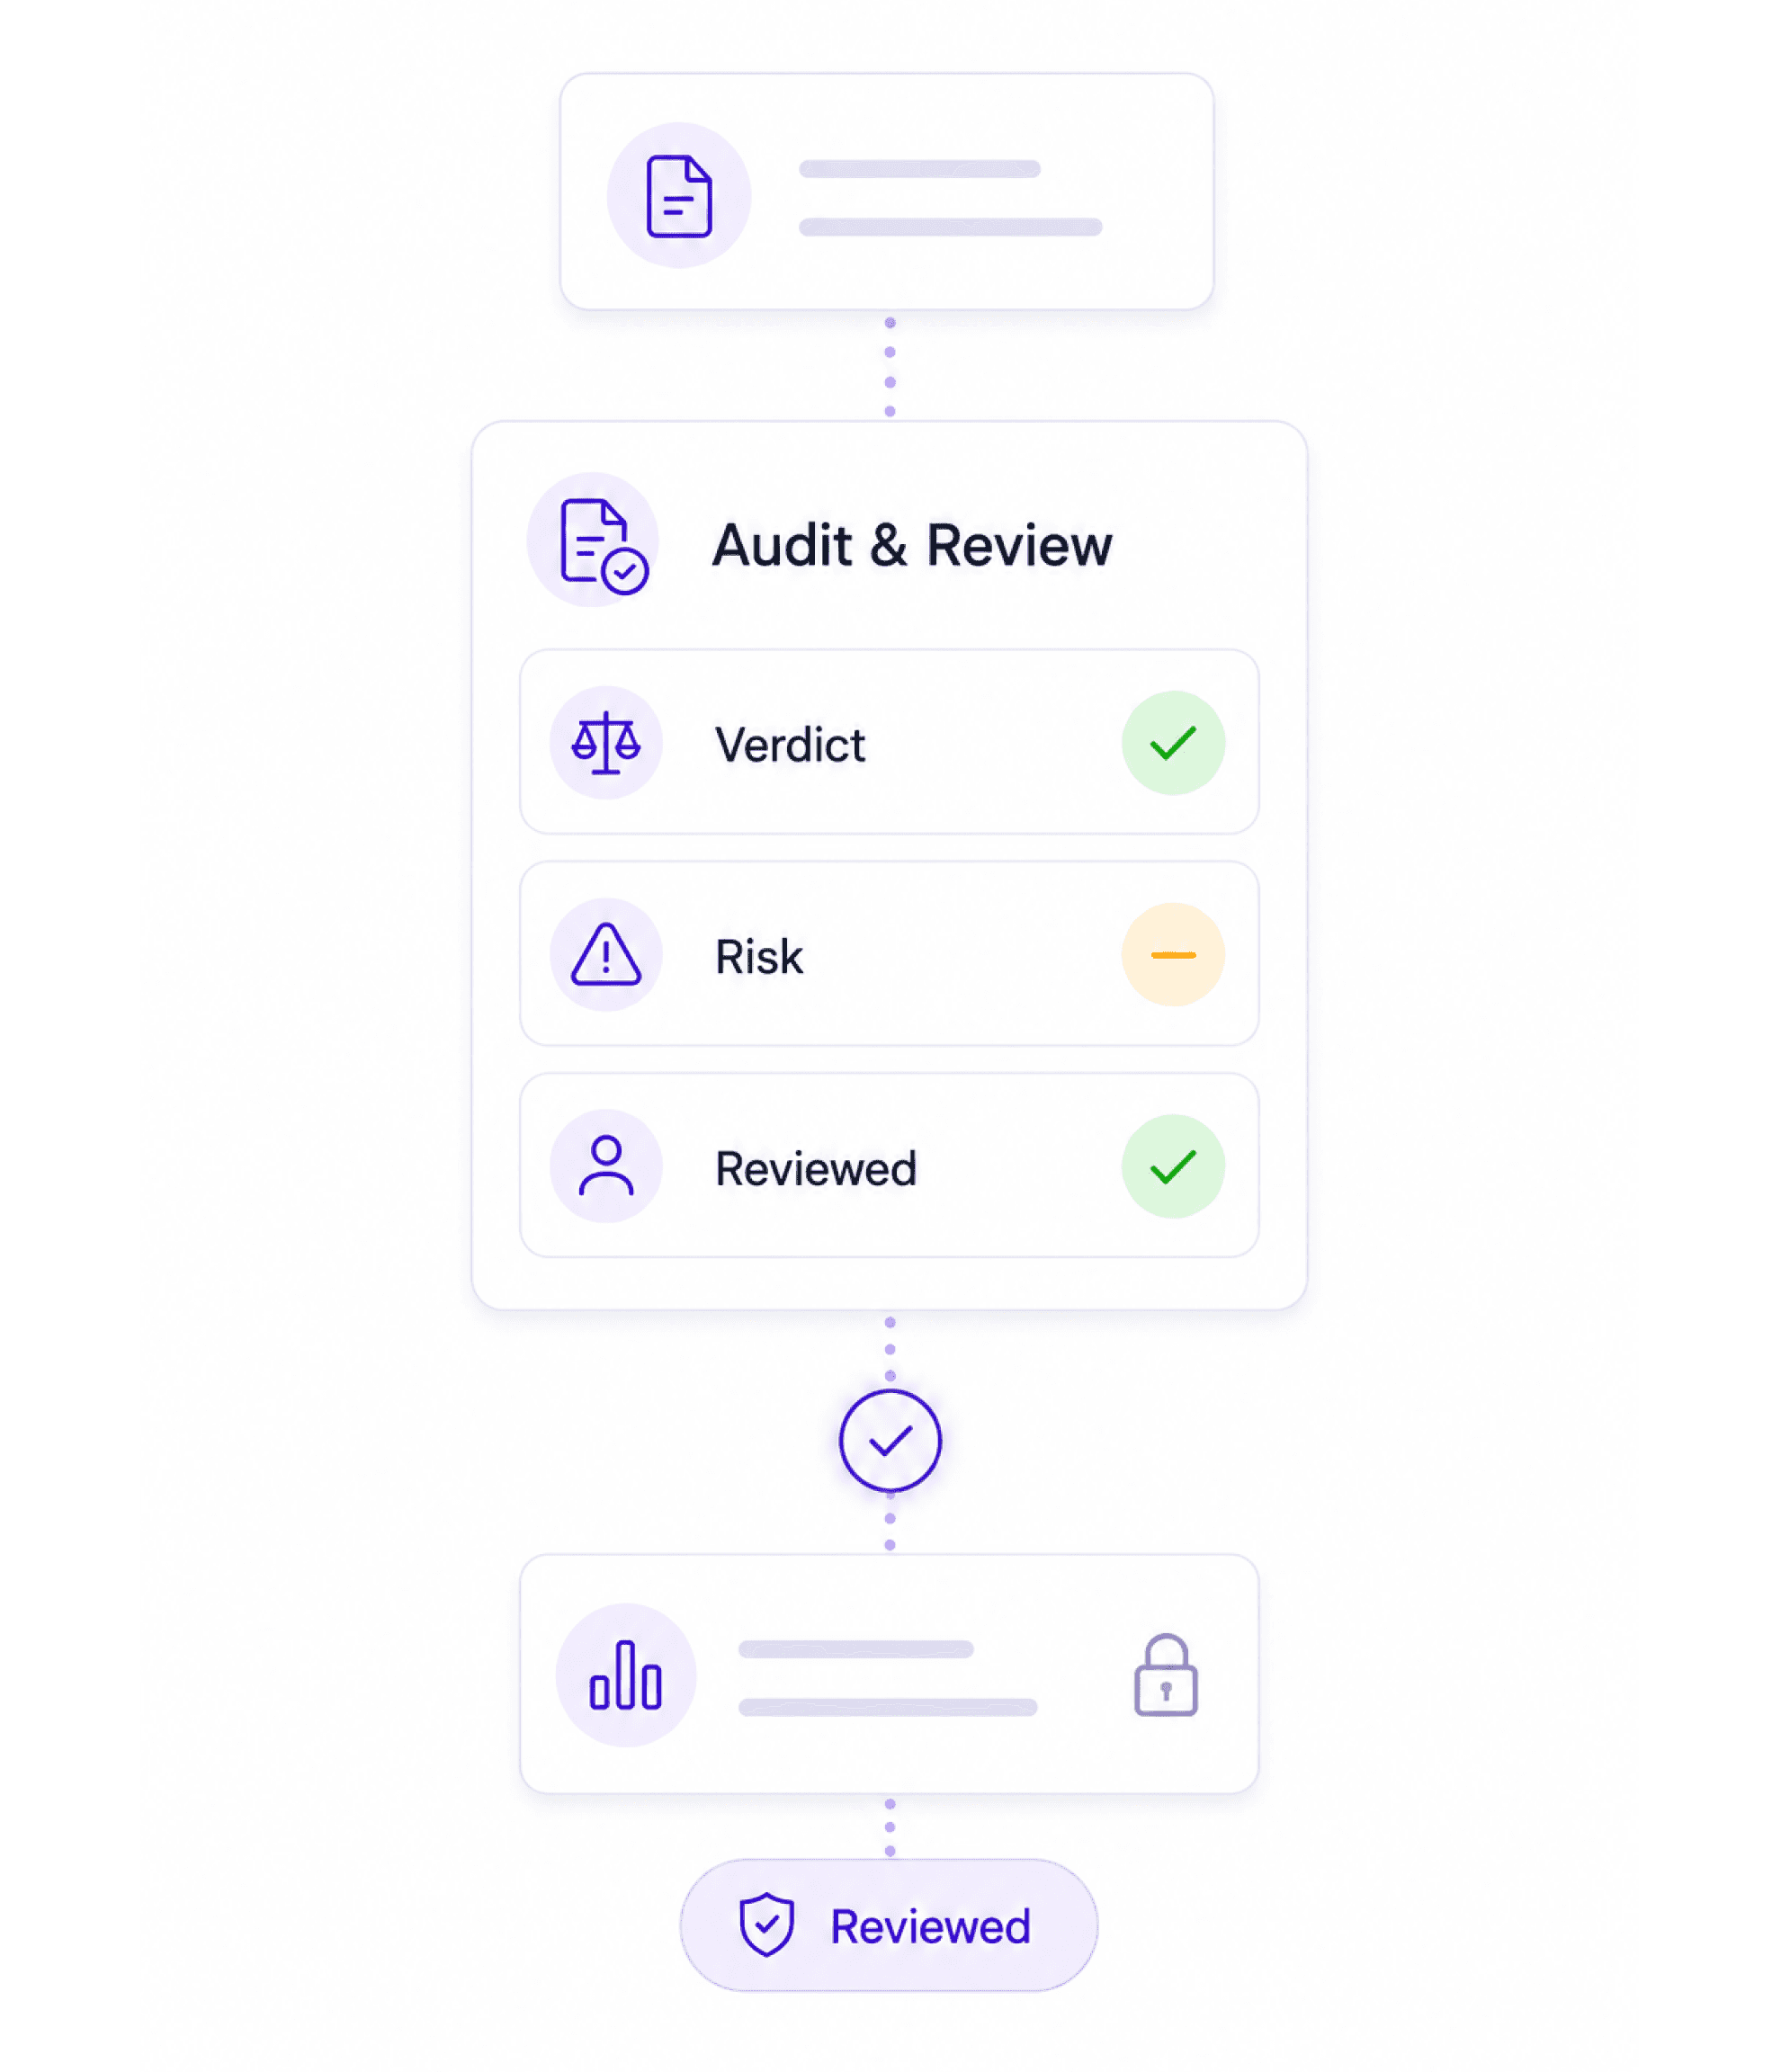
Compliance gaps
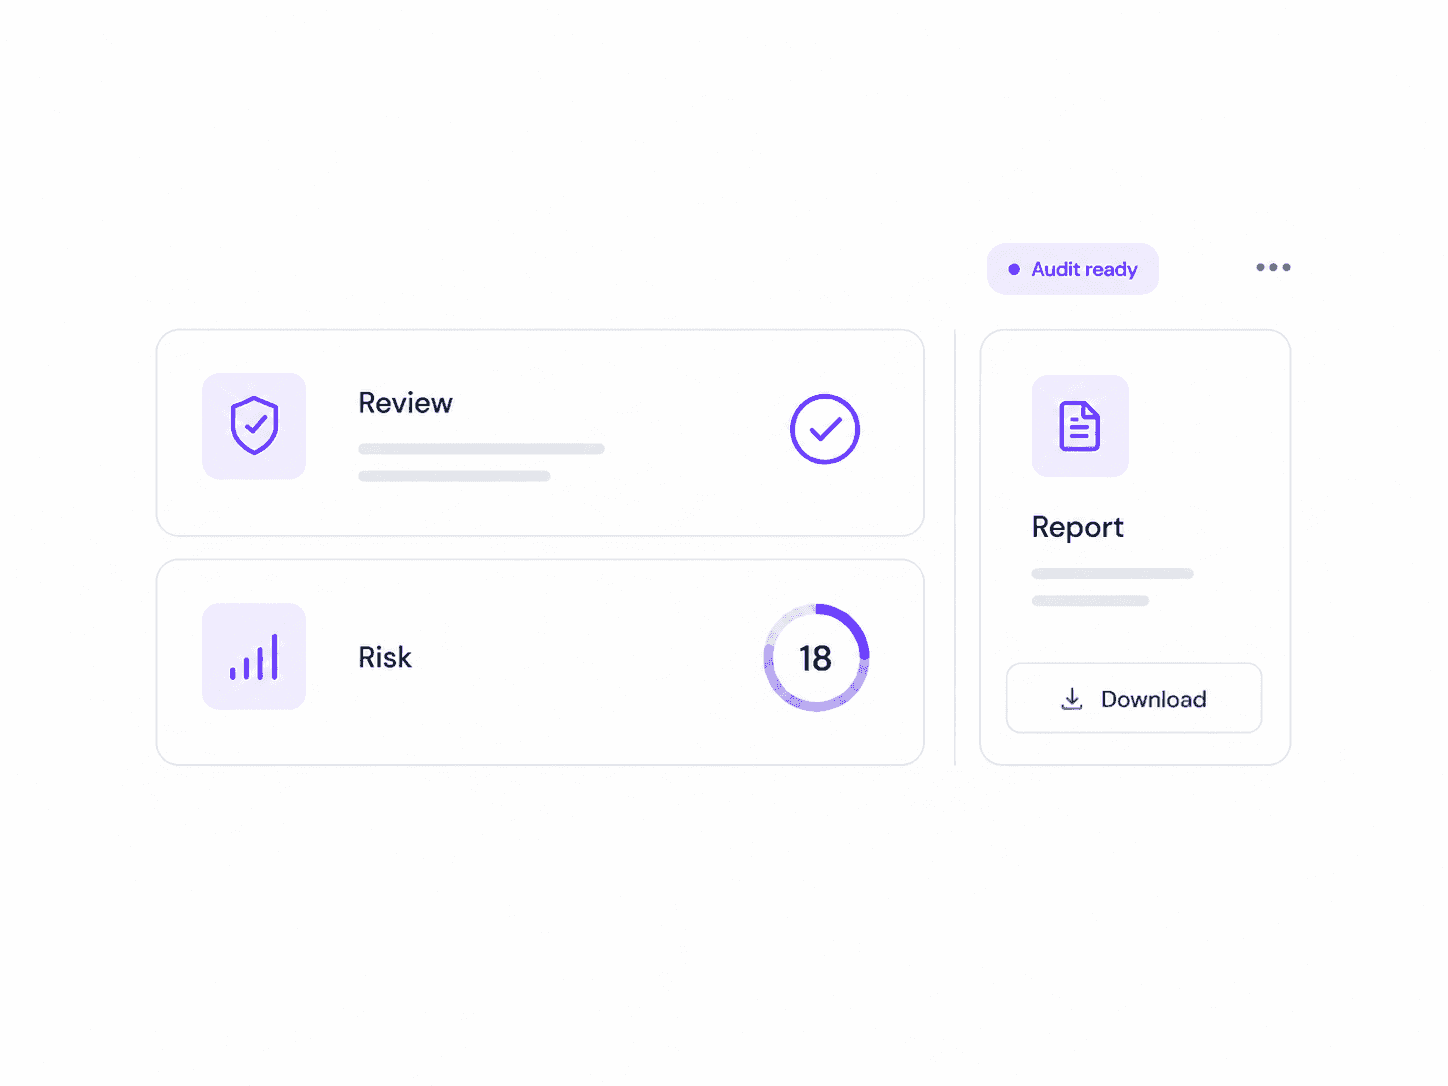
Keep AI decisions reviewable with policies, risk scores, audit logs, and reports.
Set up guardrails in three steps
Connect your LLM app, define policies, and review every decision from one workspace.
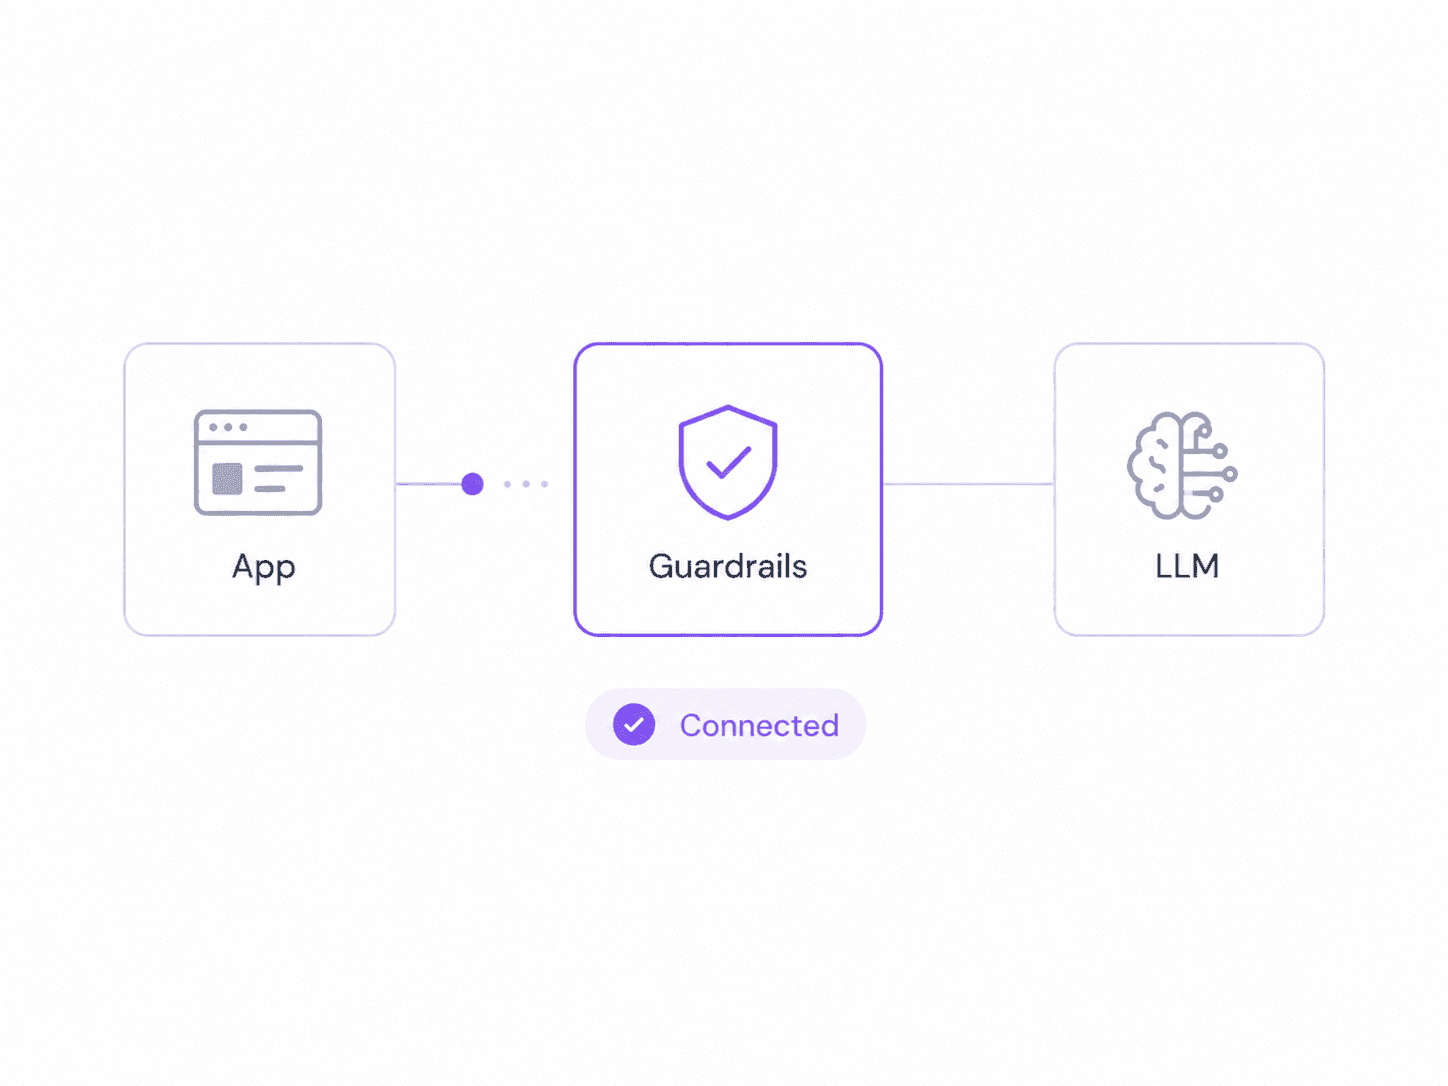
Connect your AI workflow
Route LLM traffic through a familiar gateway pattern while keeping your application flow simple.
- OpenAI-compatible endpoint
- Project-level API keys
- Python, TypeScript, and cURL snippets
- Policy assignment per project
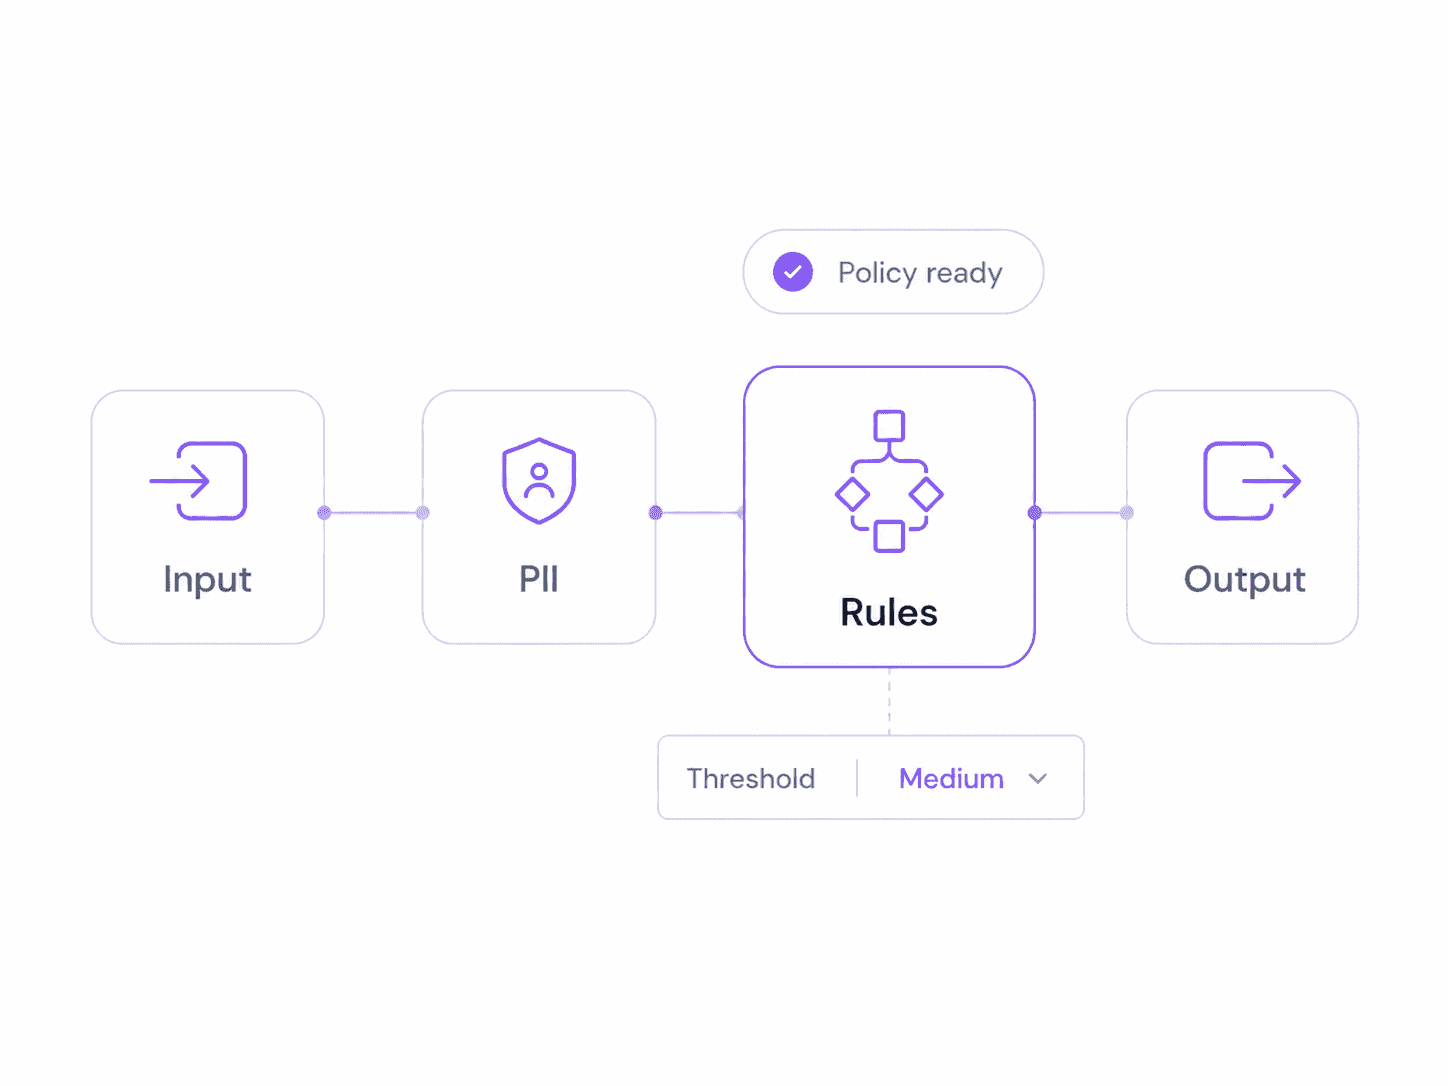
Define your policies visually
Create guardrail pipelines with configurable blocks, thresholds, actions, and sensitivity levels.
- Visual policy builder
- Input Guard and Output Guard flows
- Detection blocks
- Threshold and action settings
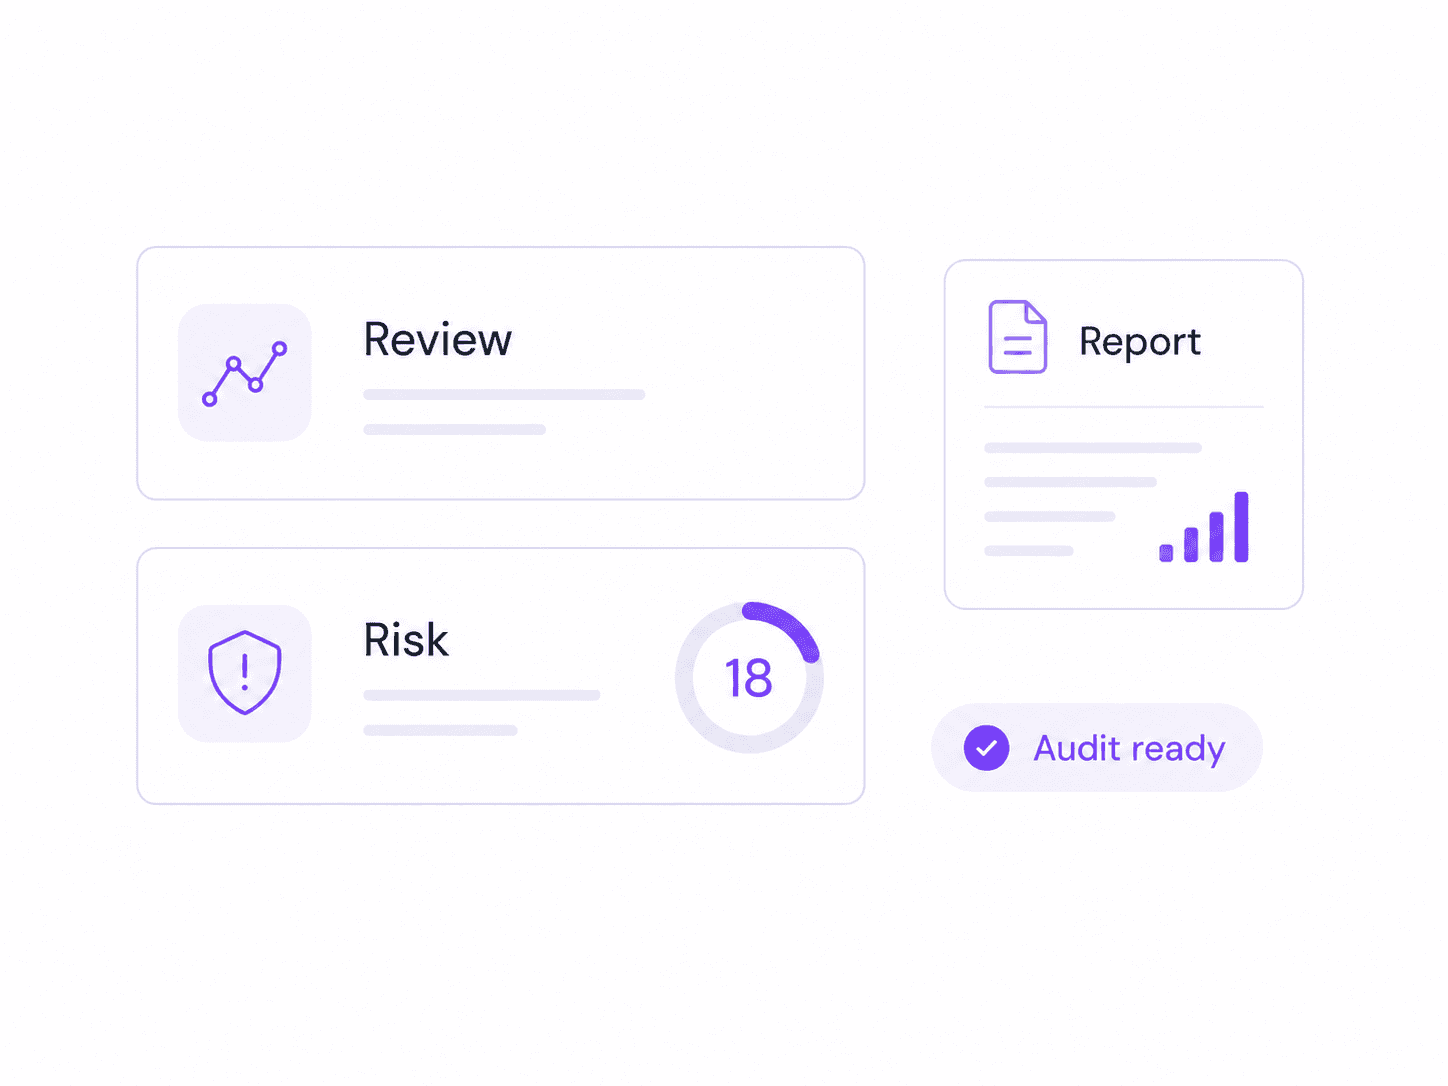
Review what happens
Use playground tests, logs, red-team runs, and reports to understand how your AI behaves.
- Playground testing
- Risk scores and verdicts
- Pipeline traces
- Audit-ready reports
Build policies without code
Create guardrail pipelines with configurable blocks, thresholds, and actions. Help security and compliance teams define AI rules without waiting on engineering.
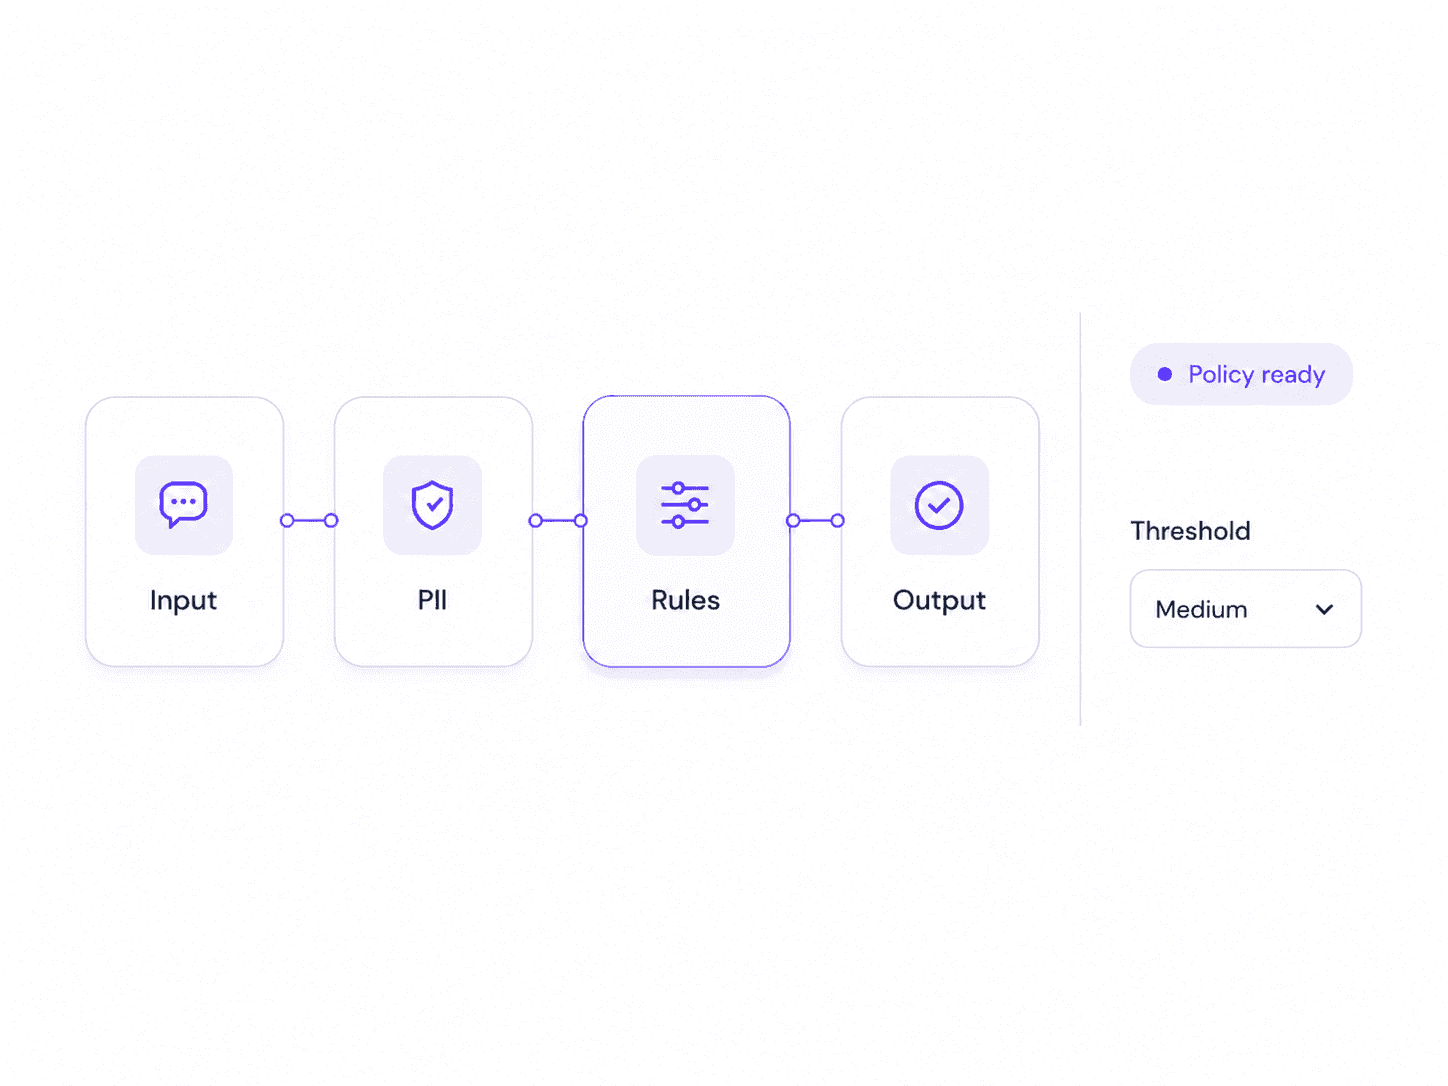
Mask sensitive data early
Detect personal data, financial identifiers, and technical secrets before they appear in prompts, responses, or stored logs.
Make every decision traceable
Review verdicts, risk scores, triggered rules, and pipeline stages so teams can understand what happened after each AI interaction.
See Guardrails in action
Test policies, inspect risky prompts, and review the audit trail before your AI reaches production users.
Request demoFrequently asked questions
Everything your team may want to know before reviewing Guardrails.
Ready to review your AI risks before launch?
Show us your LLM workflow. We’ll help you understand where Guardrails fits.